
A developer tool by Flavio
Waiting Lists
Collect confirmed subscribers with your own forms, dashboard and agent CLI, on your own Cloudflare account. One endpoint per product.
Buy Waiting Lists · $20One-time purchase. Tax included. Source code included.
Node.js 22.12+ · Cloudflare Workers, D1 and Email Service
You built something over the weekend with a coding agent. Before you show it to everyone, you want to know if anyone cares. So you put up a landing page with an email field.
The HTML form takes five minutes. Then come the questions. Did they agree to get updates? Did they confirm the address? Did the confirmation email arrive, or bounce? How do they remove themselves? What do you export on launch day?
Waiting Lists is a self-hosted service for collecting confirmed subscribers before a launch. It gives every project its own waiting-list endpoint.
Your site keeps the form you already designed. It sends an email address and explicit consent to Waiting Lists. The service handles confirmation, delivery tracking, storage, removal and exports.
Waiting Lists is built for coding agents. Give your agent one instruction. It can create a list, connect the form, check how many people joined, change the settings, and export the confirmed subscribers.
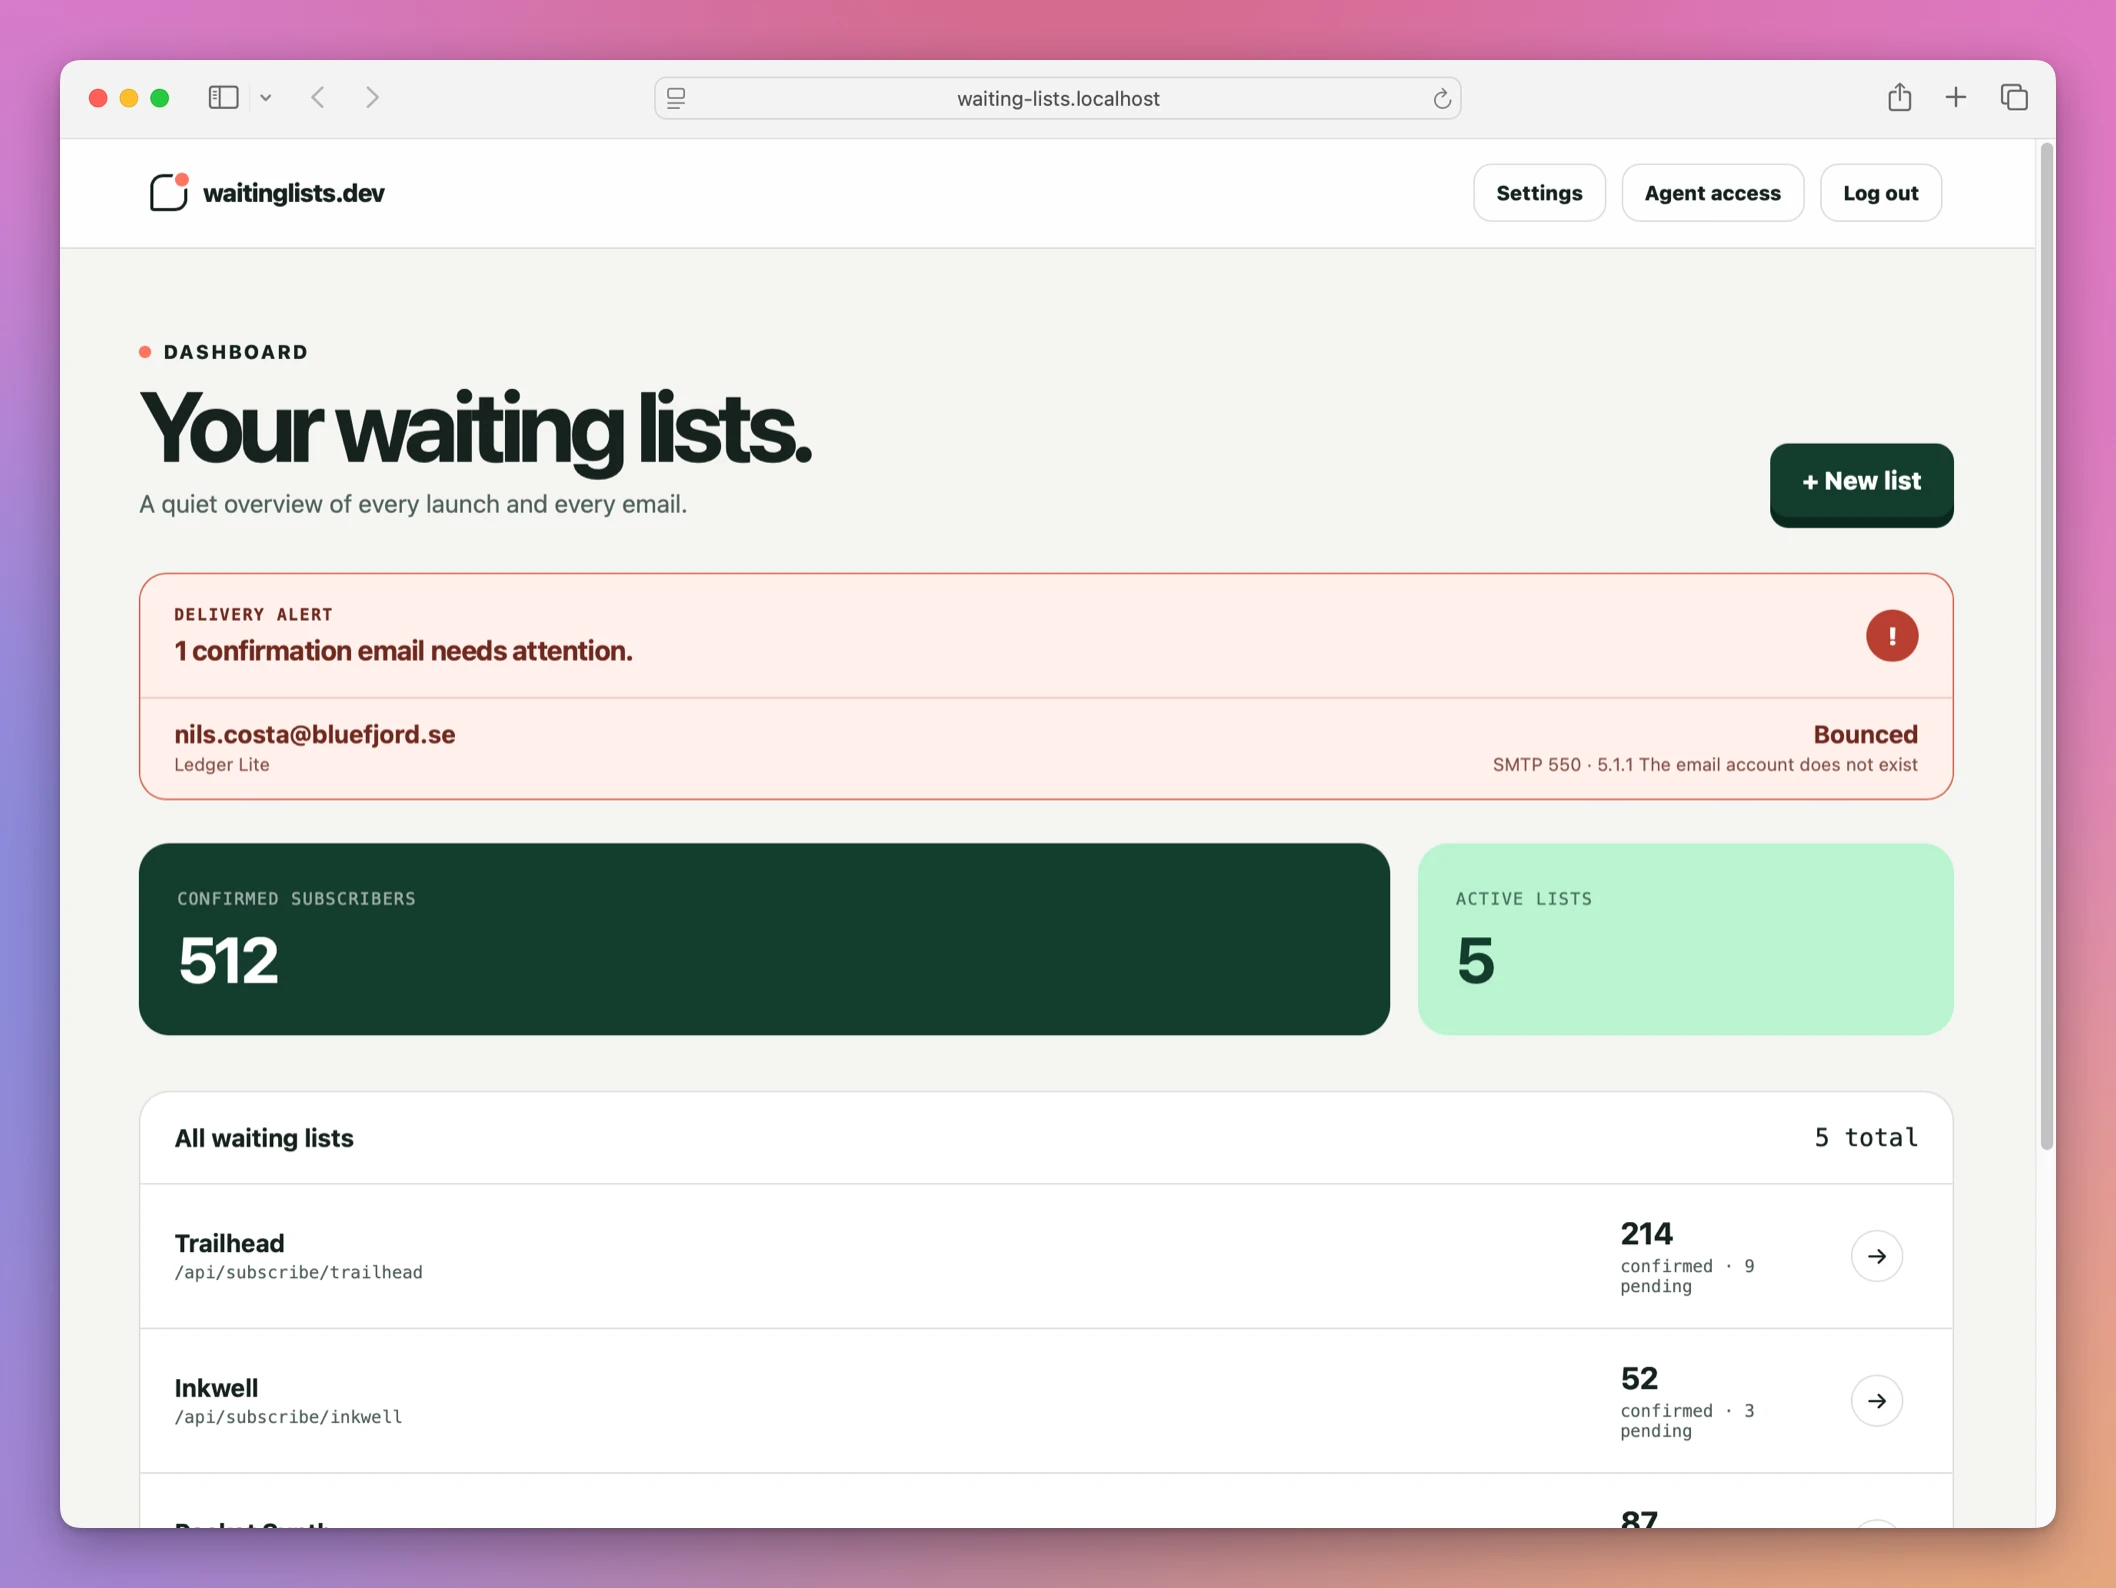
Here’s a run through a local copy with five fictional product lists: the dashboard, a signup with double opt-in, and the agent CLI:
The products, subscribers and addresses are fictional. Running locally, the confirmation email is saved as a file instead of being sent.
The form on the waitinglists.dev homepage already uses Waiting Lists. The product is collecting its own waiting list.
Who it’s for
- Indie hackers with a new idea every month. Each idea gets its own list and endpoint in the same dashboard. You don’t set up a newsletter account, a form and a confirmation flow for something you may drop in two weeks.
- Developers who build with coding agents. You tell the agent “add a waiting list to this page”, and it runs
waitinglists init, writes the form and saves the endpoint in the project. The secret key stays outside the repository. - People already on Cloudflare. Your sites run on Workers or Pages. The waiting list runs next to them, in your account, with D1 for storage and Email Service for the confirmation.
- Makers who care about consent. A security scanner that opens the link in an email shouldn’t count as a confirmation. Here the address is confirmed only after the person presses a button, and the export has the consent version and timestamps.
- Anyone who wants a private preview. The product works, but you only want to show a small part while you keep testing. The list collects interest until you’re ready to invite people.
From idea to launch day
Here’s a list for a fictional Garden Planner app, once your installation is deployed.
-
In the project folder, ask your agent to add a waiting list. It runs:
waitinglists init \
  --name "Garden Planner" \
  --origin "https://garden.northstar.example"
The command creates the list, restricts browser submissions to that origin, and saves the public endpoint in
.waitinglists.json. -
The agent adds a form to the landing page with two fields,
emailandconsent, posting to that endpoint. The list’s page in the dashboard, orintegrationin the CLI, gives the HTML or JavaScript for it. -
Deploy the page and submit an address you control. The confirmation email arrives with a link to a page with a Confirm my place button. Press it.
-
Open the dashboard. The address is confirmed, with its confirmation email marked as delivered.
-
Over the next weeks, check the confirmed and pending counts, and resend a confirmation that bounced or was rejected, with a fresh link.
-
On launch day, export the confirmed subscribers in the format your email tool imports:
sendy,kitormailchimp.
Without it, steps 3 to 6 are a confirmation flow, a token table, a bounce handler, a cleanup job and an export you’d write for each product. Here they’re the same for every list.
Why I built it
I built a lot of products during this Summer of Code. Almost every one needed the same thing before launch: a waiting list.
Until now I used Sendy for this. Sendy works well for my newsletters, but creating a list for every new idea became a bulky process. I had to create another list, set up all the pieces, connect the form, check the confirmation flow, and repeat the same work for the next product. That’s a lot of setup for an idea when I don’t know if people want it yet. I could also use a form builder or a CRM, but a waiting list doesn’t need to become a marketing system.
Coding agents let us build a ton of things, but building something quickly doesn’t mean we should immediately distribute the complete product to everyone. Sometimes we want to see if there’s demand before building further. Sometimes the product already works, but we only want to show a small preview while we keep testing it privately. A waiting list gives us that middle step.
I wanted one quiet place for all my launches, with an endpoint for each product and a small dashboard. The final export should contain only confirmed addresses. I summarized the idea like this:
Tell your agent. Launch your list.
Deploy your own copy
I distribute Waiting Lists as self-hostable software instead of a closed service you can only use through my dashboard.
The ZIP includes the compiled Worker, static assets, D1 migrations, the CLI and deployment instructions. Your Worker, database, email configuration, domain and subscriber data live in your Cloudflare account. The version running at waitinglists.dev is the reference implementation.
The download also includes the private JSON API and command-line client for your own installation. You can give the project to your agent and customize it in any way you want.
Your frontend stays yours
Waiting Lists gives you an endpoint rather than a widget you need to restyle.
A normal HTML form is enough. This example uses the reference service; replace its URL and list slug with the endpoint from your own installation:
<form
  method="post"
  action="https://waitinglists.dev/api/subscribe/my-product"
>
  <input type="email" name="email" required />
  <label>
    <input type="checkbox" name="consent" value="yes" required />
    I want updates about this product.
  </label>
  <button>Join the waitlist</button>
</form>
Each list has its own name, endpoint slug, and allowed browser origins. The www and non-www versions of a site are different origins, so add each one you use.
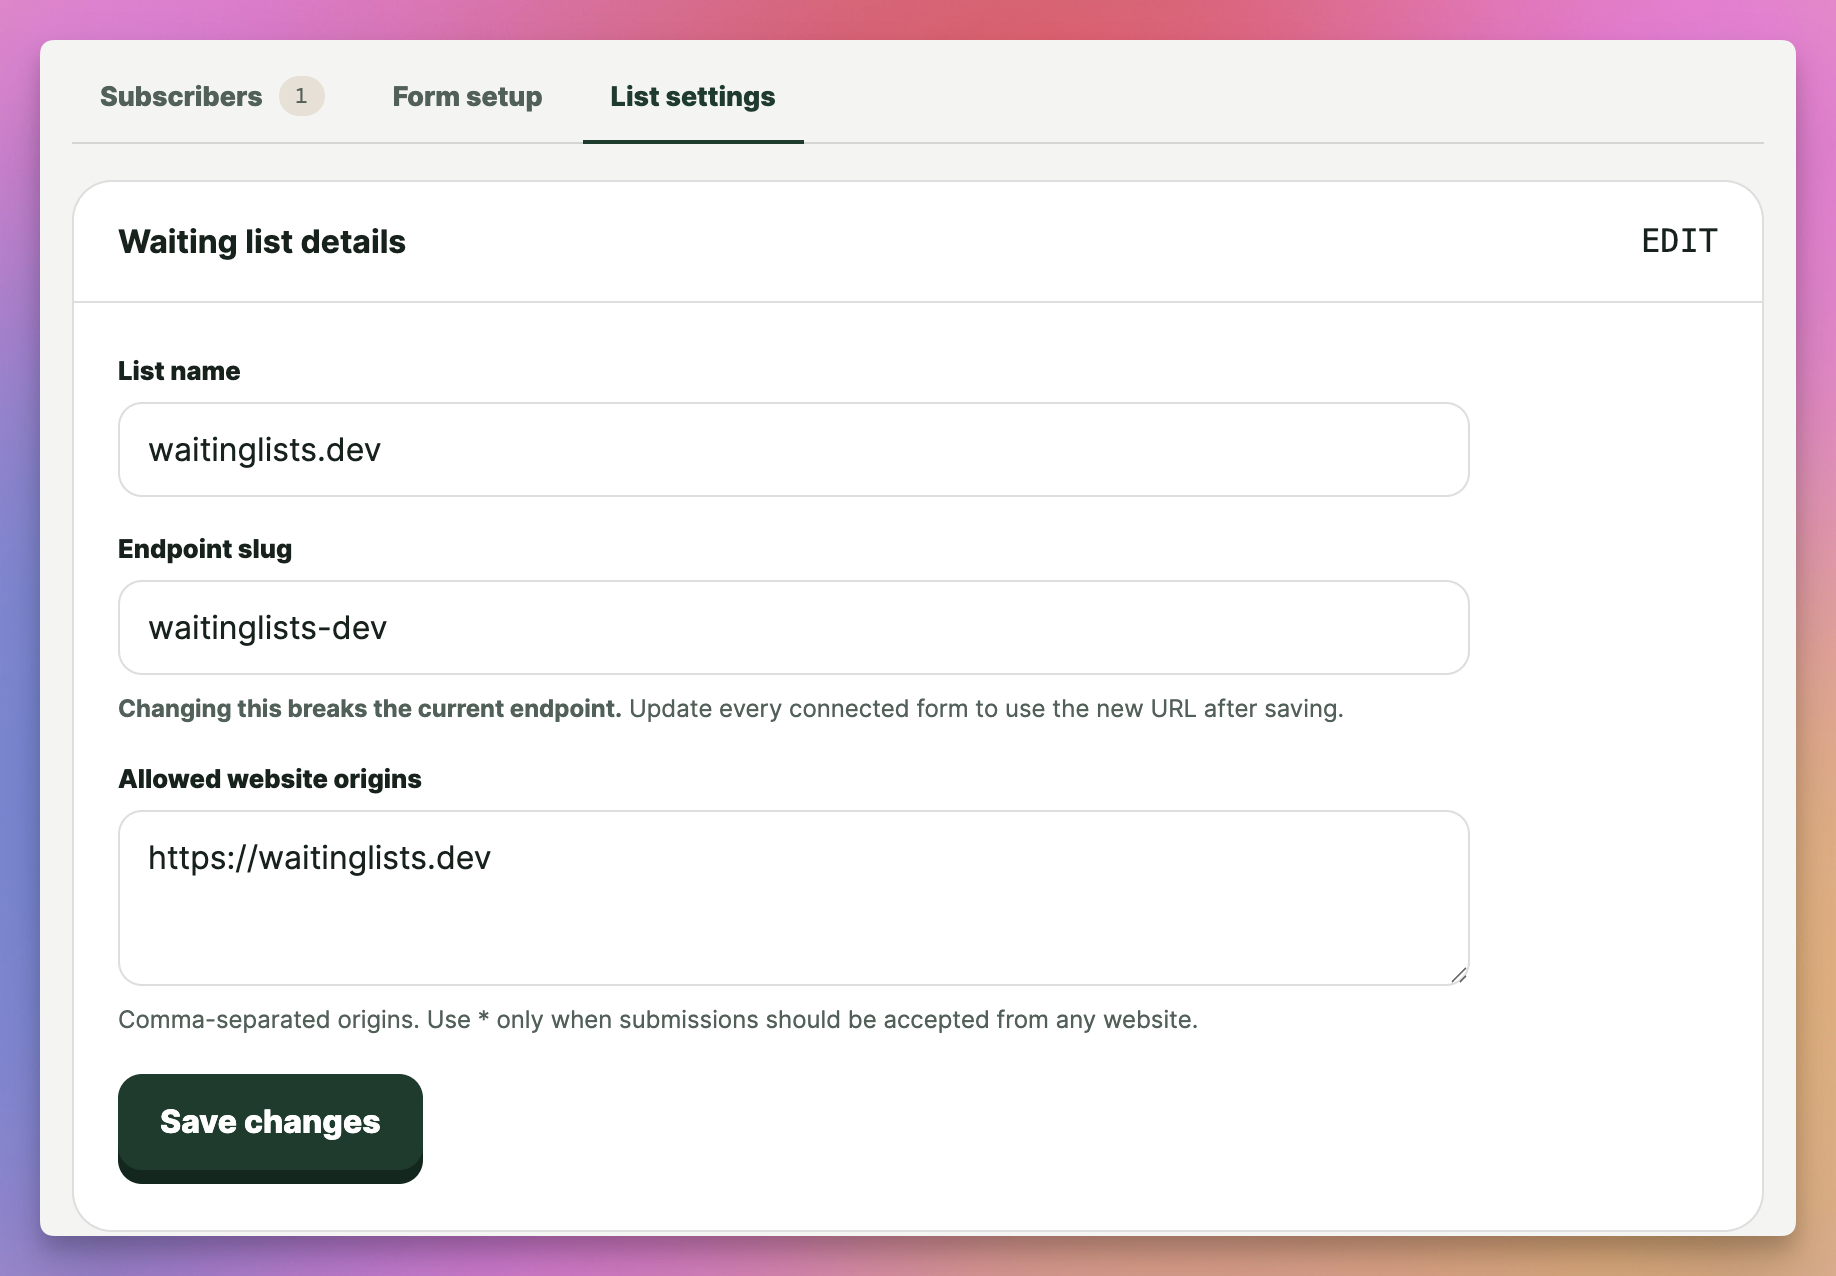
The endpoint accepts exactly two fields: email and consent. It doesn’t accept a name, profile, custom metadata, or anything else that might quietly turn into personal data I didn’t need. The tutorial on connecting a plain HTML form goes through it step by step.
After signup, the address is pending. The person receives a confirmation email. Only confirmed subscribers appear in usable exports.
The dashboard shows confirmed and pending counts, confirmation delivery status, and failures like bounces or rejections. I can resend a failed confirmation with a fresh link.
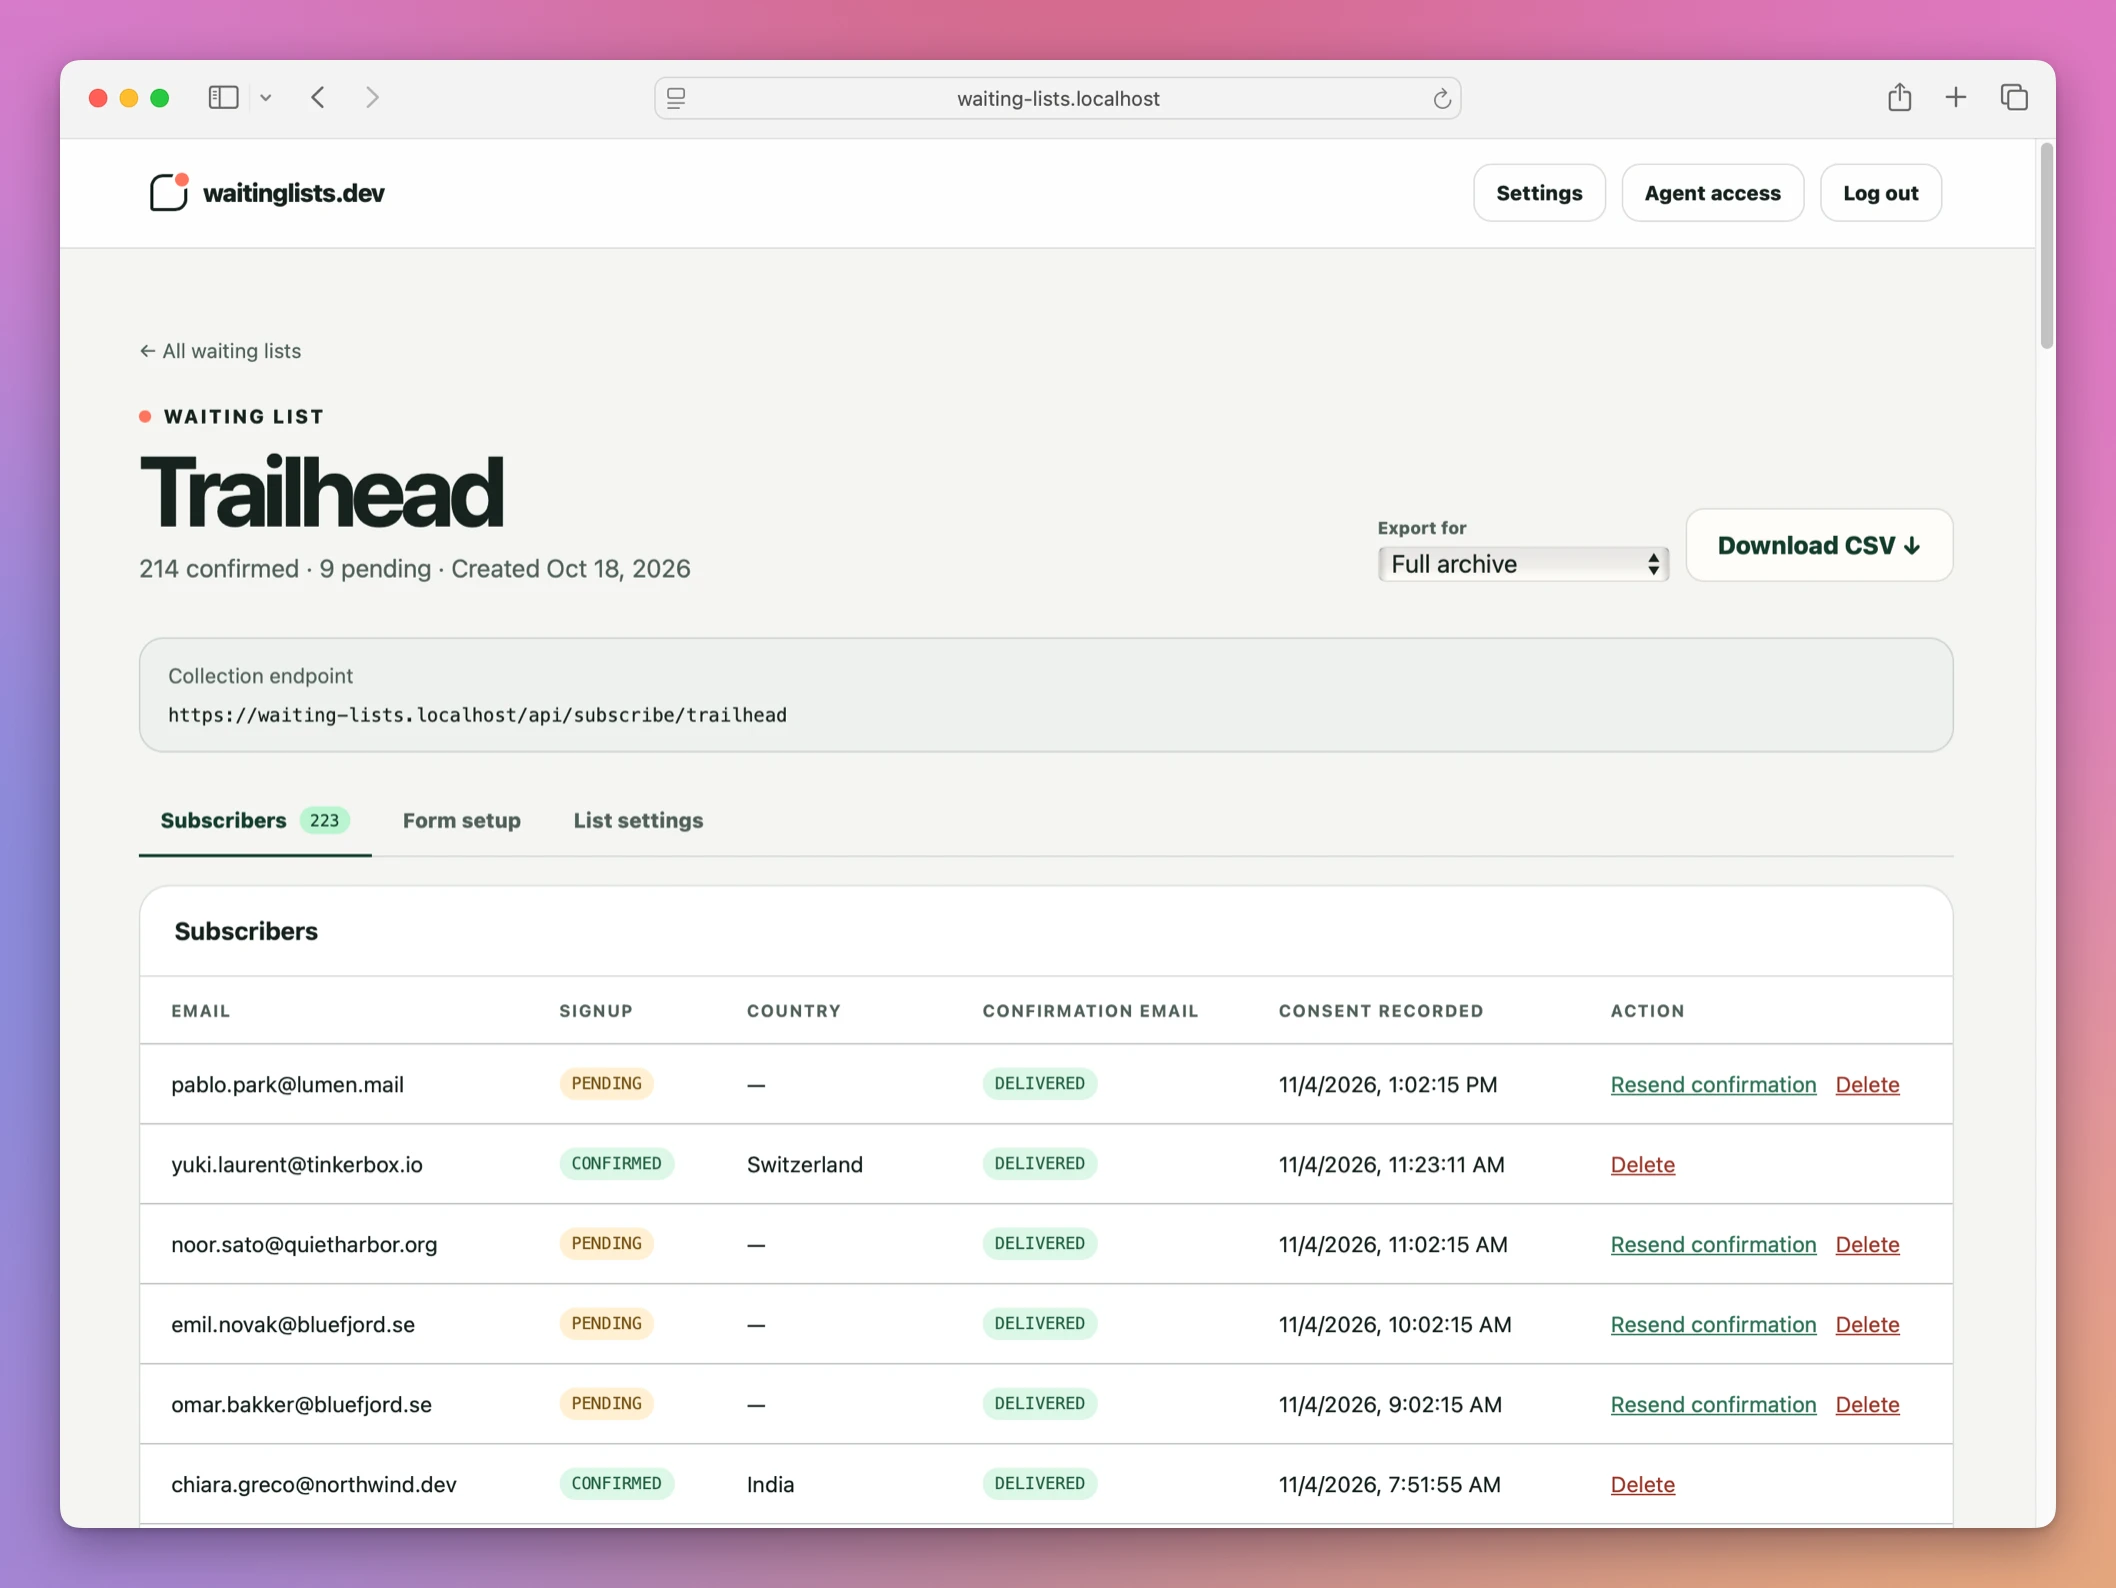
When I’m ready to launch, I can export a complete consent archive or a file prepared for Sendy, Kit, or Mailchimp.
The agent becomes the dashboard
The included command-line interface operates the private JSON API on your installation. It can list your lists, show one, update its settings, print its integration code and export it.
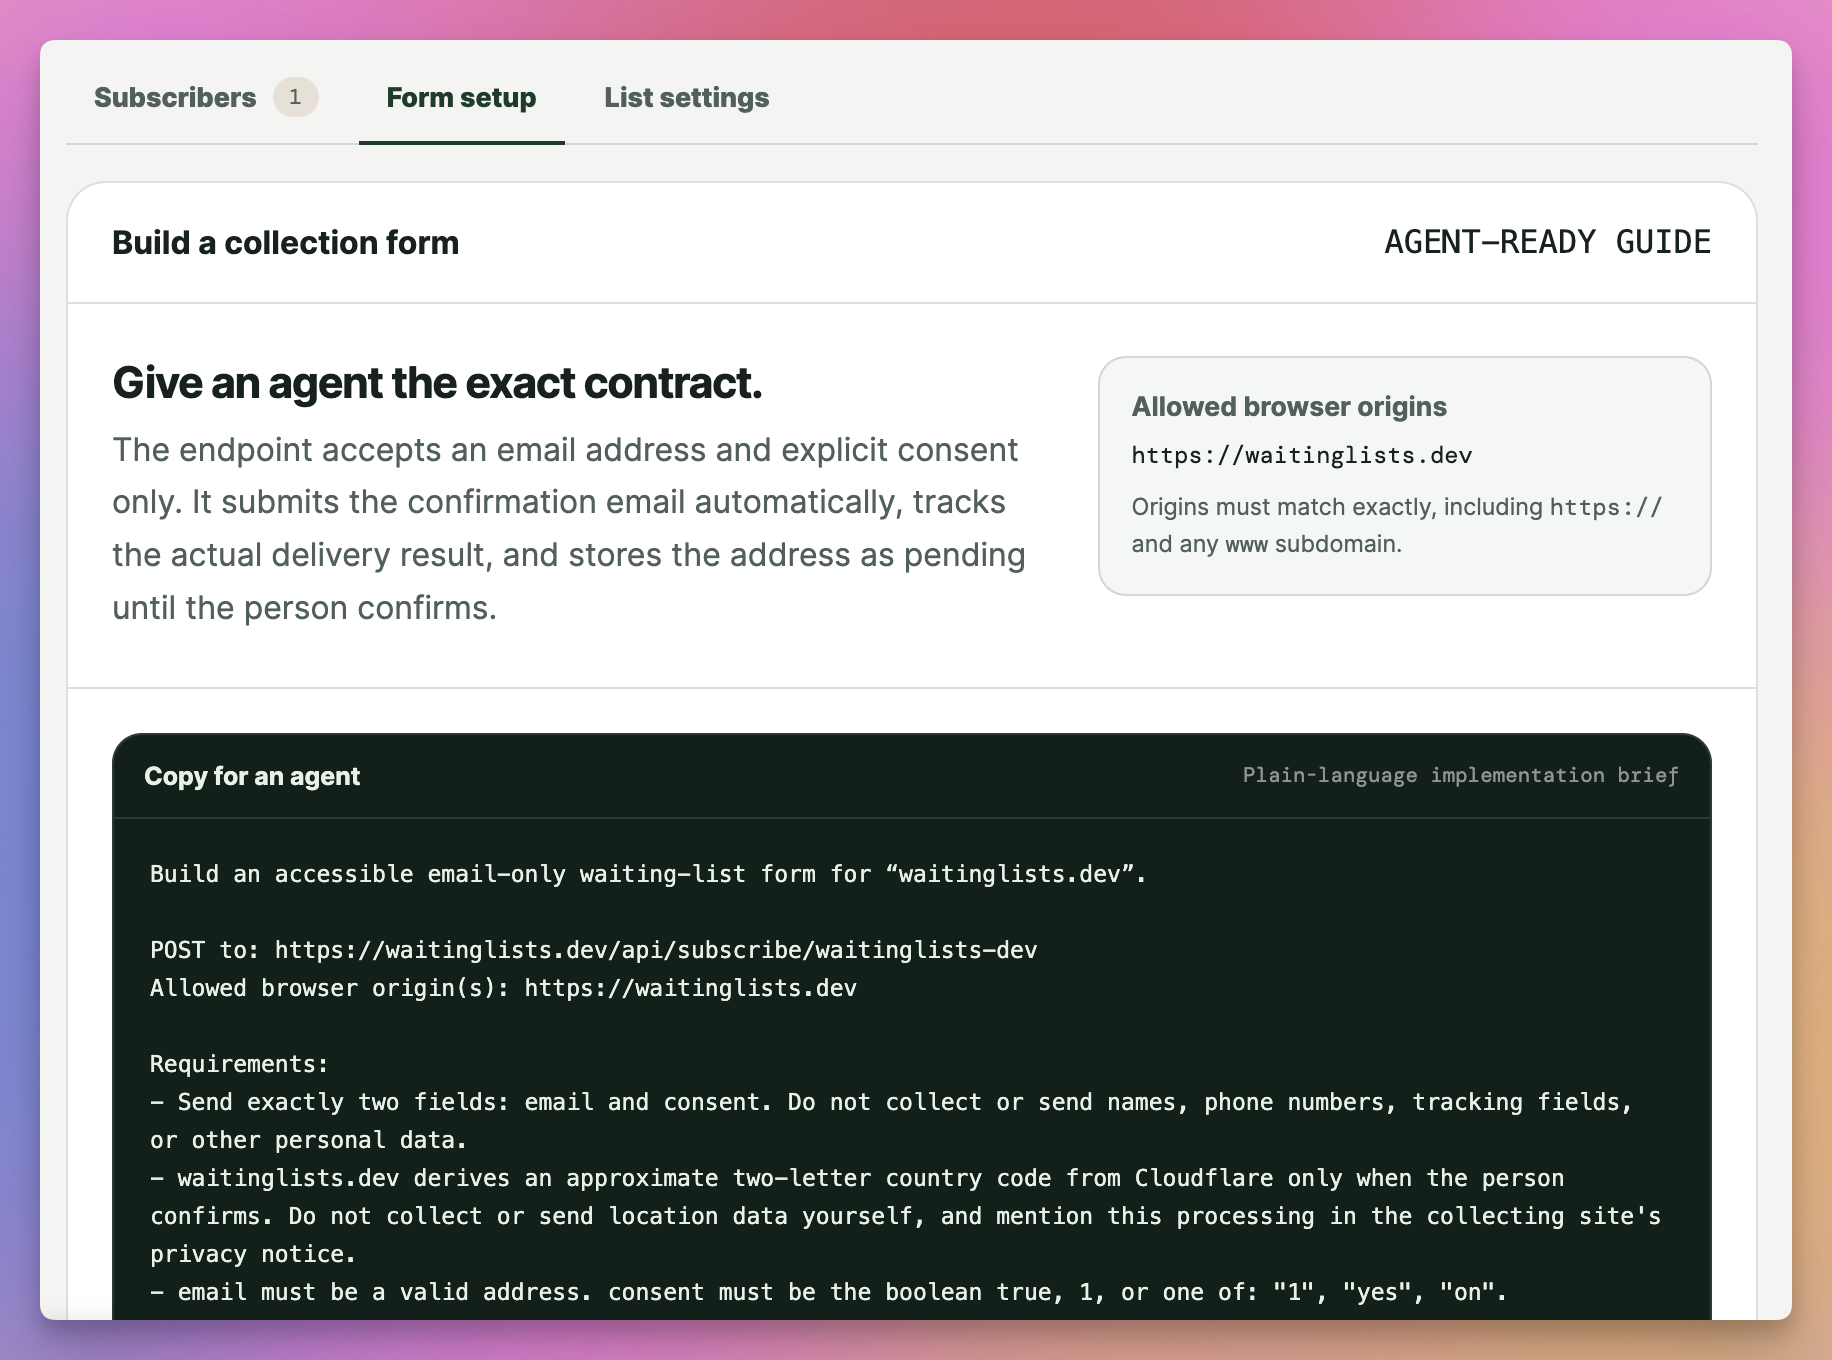
The secret API key is stored outside the repository, in ~/.config/waitinglists/credentials.json. The project file contains only the list ID, slug and collection endpoint.
Exports are handled carefully too. Subscriber data is never printed in the terminal. The agent must write it to a new file, with private file permissions, and it can’t overwrite an existing export by accident. I designed the API to be easy to call while making the unsafe action harder.
Double opt-in has a surprising problem
The basic double opt-in flow looks simple: someone submits an email, the service sends a confirmation link, the person opens it, and the address becomes confirmed.
But email security systems also open links. They scan messages before the person reads them. If opening the URL confirms the address, a security scanner can join the waiting list on the person’s behalf.
So the confirmation link opens a page with a Confirm my place button. The address is confirmed only after the person presses that button and sends a POST request.
The confirmation token contains 256 random bits. I store only its keyed hash in D1. It expires after 24 hours and works once.
Repeated signups are idempotent. An already confirmed address stays confirmed, while a pending address doesn’t receive a new message every time someone submits the form. The public response is deliberately generic too. It doesn’t reveal whether an address already exists.
The double opt-in tutorial walks through the whole flow on your own Cloudflare account.
Sending an email is not delivering an email
The Worker sends confirmation messages through Cloudflare Email Service, with a restricted binding. Cloudflare manages the sending SPF, DKIM, bounce MX and DMARC records for the domain.
Submitting a message returns an ID. It doesn’t mean the message reached the inbox. Delivery, deferral, bounce, rejection, complaint and failure events arrive later through a Cloudflare Queue. The Worker consumes those events and updates the dashboard.
An email event can arrive before the request has finished connecting its message ID to the D1 delivery record. If the Queue consumer can’t find the message yet, it waits and retries instead of discarding the event.
If someone confirms through the emailed link while delivery tracking still says processing or deferred, I treat the confirmation as stronger evidence. The dashboard marks the message as delivered.
Minimal data by design
Waiting Lists stores the email address, list relationship, confirmation status, consent version, and request and confirmation timestamps.
At confirmation time it also stores Cloudflare’s approximate two-letter country code. It doesn’t keep the IP address used to derive it. It doesn’t store subscriber names, profiles, user agents or browsing history.
Pending requests are deleted after their confirmation link expires. Confirmed records are deleted after 24 months at the latest. Every confirmation email also includes a signed self-service removal link, so the person can permanently delete the address without creating an account.
I wanted the privacy rules to be part of the data model and the scheduled cleanup, not a paragraph that depends on me remembering it later.
How I built and deployed it
Waiting Lists uses the AHA Stack. Astro renders the application on a Cloudflare Worker. HTMX handles the small form updates, while Alpine.js handles local interface state.
Cloudflare D1 stores waiting lists, subscribers, consent records, delivery events, admin sessions, and private-preview API keys. Around the Worker:
- Cloudflare Email Service sends confirmation messages
- Queues report email delivery outcomes
- edge rate-limit bindings protect login and signup endpoints
- Turnstile protects the private login
- a daily Cron Trigger removes expired data
The public collection endpoint has a deliberately small surface. Requests can be at most 2 KB, must contain exactly the two expected fields, and must come from an allowed origin. Rate limits apply to both the source IP and a keyed hash of the email address.
The private dashboard uses short-lived server-side sessions, secure HTTP-only cookies, CSRF tokens and same-origin checks. API keys are shown once, stored only as hashes, and can be revoked.
The complete application is one Cloudflare Worker. It handles normal HTTP requests, the daily cleanup job, and the Queue events from Email Service. The custom domains, D1 database, Email Service binding, Queue consumer, rate limits, Cron Trigger, logs and traces all live in wrangler.jsonc.
I first deployed it manually, then added a GitHub Actions deployment, and a few minutes later switched to native Cloudflare repository builds. Now every push to main starts the production build. The service went from an empty repository to a working production system over July 30 and 31.
Building the pages was fast. Most of the work went into deciding what a confirmed subscriber means, what data not to keep, how failures appear, and how an agent can operate the system without leaking the list.
Why not use a form service, or your newsletter tool
A newsletter tool like Sendy, Kit or Mailchimp already does double opt-in, and their hosted forms work. If you run one product and already pay for one, use it.
It gets heavy with many small ideas. Each one is another list, another form, another confirmation setup in a tool built for campaigns. A plain form service collects addresses, but the confirmation and the bounce handling are still yours to build. And in both cases the subscriber data lives in someone else’s account.
| Form service or newsletter tool | Waiting Lists | |
|---|---|---|
| A list for a new idea | Set up a list, a form and the confirmation in the dashboard | A name and an origin, in the CLI or the dashboard |
| Your form’s design | Their widget, or their form fields | Your own HTML form |
| Scanner clicks on the link | Depends on the tool | Confirmed only after a button press |
| Where the data lives | Their servers | Your Cloudflare account |
| An agent setting it up | Through the dashboard | The CLI and the JSON API |
| Moving to your email tool | Already there | Export for Sendy, Kit or Mailchimp |
What it doesn’t do
- It doesn’t send newsletters. It sends the confirmation email. On launch day, export the list to your email tool.
- It doesn’t have teams or accounts. The first version is single-owner on purpose: no public account creation, team system, billing layer or campaign editor. Ask your agent to add what your installation needs.
- It doesn’t collect more than an email. No names or custom fields. The endpoint accepts
emailandconsentand nothing else. - It isn’t a hosted service. Your purchase doesn’t include a hosted subscriber service. You deploy it to your own Cloudflare account.
- It doesn’t come with Cloudflare. Cloudflare and domain charges are separate from the software purchase.
Questions
Can I try it locally first?
Yes. The Worker runs locally with Wrangler. Running locally, the confirmation email is saved as a file instead of being sent.
How many lists can I have?
Each product gets its own list, with its own endpoint slug and allowed origins, all in the same dashboard. The demo above runs five.
Does my agent see the subscribers’ addresses?
The CLI never prints subscriber data in the terminal. An export goes to a new file with private permissions, and you decide what happens to it.
What format are the exports?
Pick universal, archive, sendy, kit or mailchimp. The archive is the complete consent record. Exports are created with owner-only permissions and never overwrite an existing file.
Buy Waiting Lists
Waiting Lists costs $20 including tax, paid once. The purchase includes the ready-to-install ZIP.
Download the runtime ZIP from your purchase page. Reopen that page for later versions.
Set up your installation
You need Node.js 22.12 or newer. Unzip the download and follow the deployment guide to configure Wrangler, run the migrations, and start the Worker locally.
For production, you need a Cloudflare account with Workers, D1, Queues, Email Service and Turnstile configured for your own domain. The deployment guide covers the bindings, secrets, migrations and email setup. Cloudflare and domain charges are separate from the software purchase.